In a recent privacy breach, Telstra revealed that a technical fault exposed the personal details of over 24,000 customers with silent numbers. This incident has raised serious concerns about data security, especially for VoIP users seeking privacy. Telstra is now taking steps to enhance protections and prevent future breaches.
The Federal Communications Commission (FCC) has issued fines totaling $196 million to major US telecommunications operators for unlawfully sharing customers’ location data. This action comes more than five years after the violation was initially exposed.
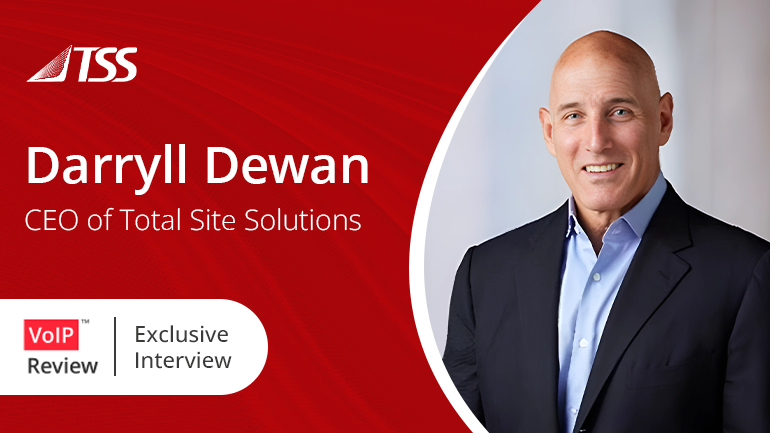
Darryll Dewan, CEO of Total Site Solutions (TSS), unveils the dynamic landscape of data centers in 2024. TSS’s report highlights key trends: modular data centers’ rise, heightened security needs, sustainability emphasis, and the widening skills gap. Dewan emphasizes adaptability amid AI-driven shifts, underscoring the need for proactive planning and collaboration.
In a recent security breach, Comcast has alerted millions of Xfinity customers about potential compromises to their passwords and portions of social security numbers. The breach, linked to a known vulnerability affecting major companies, including Boeing and Toyota, has been dubbed “CitrixBleed.”
With Vodafone’s pending merger with Three, concerns mount over potential access to sensitive UK government data by foreign entities, chiefly China. Unite the union has issued a report detailing alleged connections between Three’s controlling CK Group and the Chinese government, raising concerns over integrity of communications within governmental public sector clients served by Vodafone including the NHS and Ministry of Defence. Is the potential for this large scale data breach being overlooked? T
Four prominent Swedish companies are under the scanner for illicit data transfer to the U.S., marking a stark violation of EU’s GDPR rulings. The heart of this issue lies in their use of Google Analytics, leading to these privacy breaches. Interestingly, not all implicated parties bore the same guilt, showing varying levels of data safety vigilance. More caution and respect for GPDR’s regulations is thus urged from all companies dealing with data transfers. Undeniably, an increasing global scrutiny on data protection laws, demands such vigilance.
Ofcom falls victim to Clop ransomware attack, compromising personal data of 412 employees and confidential information of regulated companies. The breach exposes vulnerabilities in MOVEit software, prompting industry-wide reevaluation of cybersecurity measures.
Meta faces a record €1.2 billion GDPR fine for transferring European users’ data to the US, raising questions on compliance, data privacy regulations, and US surveillance laws. With Meta appealing the decision, the telecommunications industry watches closely.
When it comes to the security of your business, you can’t afford to take any chances. But what are the best ways for you to protect your data and make sure your employees are safe? One way is by using a Virtual Private Network (VPN). With more and more employees working from home, many IT professionals may decide to route Voice-over-IP (VoIP) traffic together with the user’s other data through a VPN. Using a VPN for VoIP calling provides additional levels of security and privacy, assisting both in-house and remote workers in remaining secure. What is a VoIP VPN? Simply explained, a VoIP VPN will build a secure tunnel through which all of your VoIP communications will traverse. As a consequence, you’ll be able to circumvent firewall limitations and make calls in a secure manner. Additionally, this type of service will conceal your actual IP address and allocate a…
More than 130,000 Telstra customers’ personal information has been made public online. According to the company, there was no cyberattack involved; rather, the issue was caused by a “misalignment of databases” as stated by Telstra. The incident is the most recent in a string of massive, unauthorized exposures of personal information in Australia. The telecom giant confessed that the information, which included the names, addresses and phone numbers of customers who had requested that their information be kept confidential, had been published on the White Pages and Directory Assistance Services websites. Telstra’s routine auditing procedures revealed the data leak. Following the finding, Telstra began contacting affected consumers and is providing free identity theft protection services. The corporation claims to have since deleted the consumer information from public view. “Protecting our customers’ privacy is absolutely paramount, and for the customers impacted we understand this is an unacceptable breach…